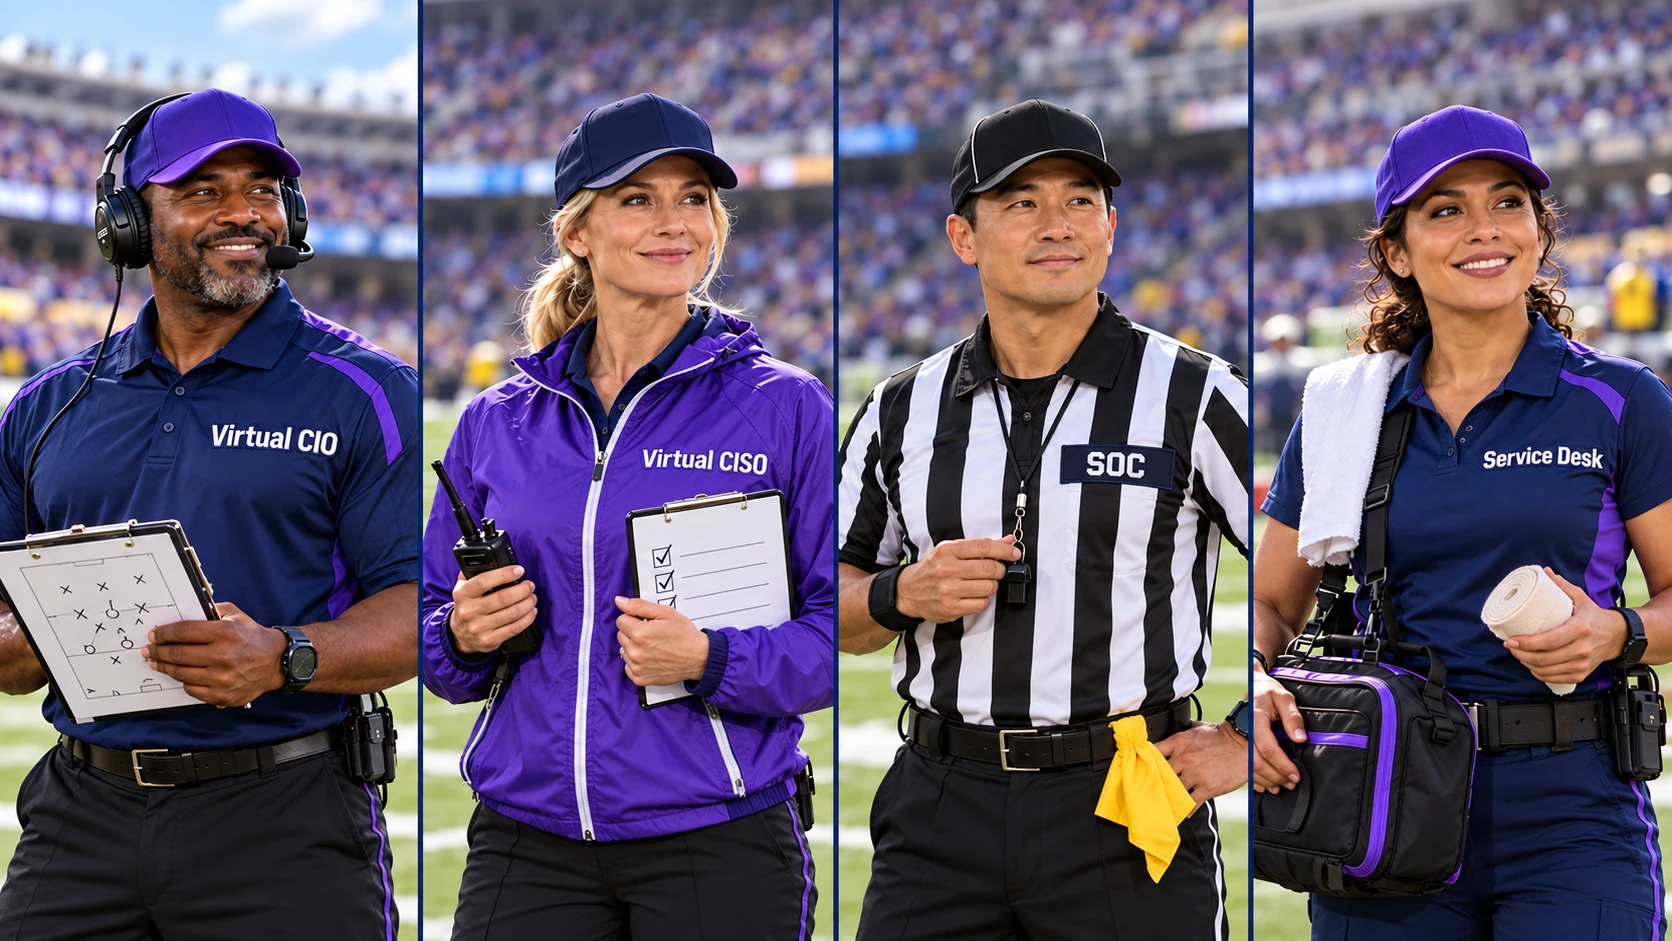
“Call IT” Is Not Always Specific Enough
Technology and cybersecurity come with no shortage of acronyms. For many organizations, terms like IT, vCIO, vCISO, and SOC can start to sound like alphabet soup.
The confusion is understandable. In day-to-day operations, “Call IT” might mean fixing a printer, unlocking an account, troubleshooting an application, reviewing a suspicious email, or helping leadership think through technology and cyber risk.
In healthcare, you would not go to an orthopedic surgeon for a stomach issue. In banking, you would not treat a teller, loan officer, investment advisor, or fraud analyst as the same role just because they all work with money. Each has a different focus, purpose, and role.
The Simple Difference
What is the Difference Between vCIO and vCISO? What is the Difference Between IT Service Desk and SOC?
Although these functions often work together, they serve different purposes. The easiest way to separate them is to look at the type of question each one helps answer.
| Function | Main Focus | Plain-English Role |
|---|---|---|
| vCIO Virtual Chief Information Officer | Technology strategy and planning | Helps leadership decide where technology needs to go |
| vCISO Virtual Chief Information Security Officer | Cybersecurity risk and governance | Helps leadership understand, prioritize, and manage cyber risk |
| IT / Service Desk User Support | Daily support and operations | Keeps users, systems, and technology working |
| SOC Security Operations Center | Security monitoring and response | Proactively watches for threats and helps respond when suspicious activity is detected |
These roles are connected, but they are not interchangeable.
What This Looks Like in Real Life
A login issue may start as an IT ticket. If the activity looks suspicious, the SOC may investigate. If it points to a broader identity risk, the vCISO may help leadership prioritize next steps. If the fix requires investment, the vCIO may help place it into the roadmap and budget.
The same applies to larger projects, such as a cloud migration, office expansion, vendor change, or new business application. These are not just IT projects. They involve business planning, security risk, operational support, and ongoing monitoring.
When the roles work together, organizations are less likely to miss the handoff between support, planning, risk, and response.
Where Role Gaps Show Up
The real issue is not the acronym. It is the handoff. Each function supports a different type of decision.
If a workstation is not working, that is usually an IT support issue. If a system is outdated, that becomes a technology planning issue. If it creates security or compliance risk, that becomes a cybersecurity governance issue. If suspicious activity is detected, that becomes a monitoring and response issue.
When all of these are treated as simply “IT,” important questions can get missed:
- Who is responsible for the immediate fix?
- Who determines whether the issue is part of a larger trend?
- Who explains the business or security risk to leadership?
- Who monitors for signs that the issue is being exploited?
This is where gaps form. An organization may be able to fix individual tickets but still lack a roadmap. It may have security tools but lack governance. It may receive alerts but lack a clear process for escalation, decision-making, and response.
What If You Only Have IT Service Desk Support?
Not every organization has a separate person or service assigned to each function. In many environments, support begins with IT and an Account Manager coordinating communication, priorities, and follow-up.
That model can work well, especially when expectations are clear. The important point is not whether every role has a separate title, but whether the underlying responsibilities are understood, including where gaps may exist.
If a suspected security incident occurs, IT will usually help with the immediate technical response. They may disable accounts, reset passwords, isolate devices, restore access, check system availability, or escalate technical issues.
That support matters, but an incident may require more than troubleshooting. The organization may also need to determine what happened, whether data was accessed, whether evidence should be preserved, whether legal or regulatory obligations apply, and what leadership decisions are needed.
This is where role clarity becomes especially important. Leaders should know who handles the technical response, investigates suspicious activity, guides cybersecurity risk decisions, manages business or compliance considerations, and brings in outside expertise when needed.
The goal is to know before something happens who is responsible for what, how escalation works, and where additional support may be needed.
Why It Matters Now
Security incidents rarely stay in one lane. A suspicious login may begin as a technical issue, become a security investigation, and quickly turn into a legal, privacy, insurance, customer, or leadership concern.
External reports reinforce this point. IBM’s 2025 Cost of a Data Breach Report found that healthcare had the highest average breach cost by industry at $7.42 million, showing how quickly security and technology issues can become financial and operational events.
Verizon’s 2026 Data Breach Investigations Report found that 31% of breaches now start with software vulnerability exploitation, reinforcing why technical support, security monitoring, risk guidance, and technology planning need to work together.
For healthcare organizations, incident response may also include regulatory obligations. HHS OCR states that breaches of unsecured protected health information affecting 500 or more individuals must be reported without unreasonable delay and no later than 60 calendar days after discovery.
The takeaway is simple: organizations need clear ownership for technical response, risk decisions, threat monitoring, and leadership communication.
Questions to Ask Next
The goal is not to add complexity. The goal is to know who is responsible for what, where decisions should go, and when additional support may be needed.
Start by asking:
- Who helps us plan our technology roadmap?
- Who helps us understand and prioritize cybersecurity risk?
- Who monitors for suspicious activity?
- Who helps coordinate response if something looks serious?
- Do we know where our current gaps are?
Why it's Important to Have a Trusted MSP Partner
At Anatomy IT, we understand the IT and leadership roles, gaps, questions, and how to help our clients achieve cybersecurity resilience. Cybersecurity resilience depends on more than tools, titles, or acronyms. It depends on clear responsibilities, thoughtful handoffs, and the right people working together before disruption occurs.
Resilience improves when roles are clear, connected, and business-aligned.
We help healthcare organizations evaluate their technology environments, identify meaningful risk, and develop practical roadmaps that align technology investments with operational and business priorities.
Resources:
- IBM Cost of a Data Breach Report 2025 , 20250822_Cost-of-a-Data-Breach-Report-2025.pdf
- 2026 Verizon DBIR: Breakthroughs in vulnerabilities, AI-assisted cyber attacks and social engineering, https://www.verizon.com/business/resources/T1ae/reports/2026-dbir-data-breach-investigations-report.pdf
- Submitting Notice of a Breach to the Secretary | HHS.gov, https://www.hhs.gov/hipaa/for-professionals/breach-notification/breach-reporting/index.html